The Ultimate Guide to AI Governance Frameworks & SaaS Risk

Mar 2, 2026

blue polygon icon

Learn what AI governance is, core principles, and how to build an AI governance framework that manages risk, identity, SaaS access, and continuous oversight.

Link to Linkedin
This webinar will cover:
In this webinar:
See More
See more
Fill out the form and watch webinar
Oops! Something went wrong while submitting the form.
Register now and save your seat!
Registration successful!
Webinar link will be sent to your email soon
Oops! Something went wrong while submitting the form.
In this webinar:
See More
See more

AI adoption has outpaced AI control. In most organizations, governance is still playing catch-up.

Artificial intelligence is now embedded across SaaS platforms, automated workflows, and employee browsers. What began as individual productivity experimentation has evolved into a structural shift in how enterprise decisions are made and data is shared. Bringing order to this environment requires an operational governance framework.

Key Takeaways

  • AI governance ensures continuous visibility, compliance, and access control across all AI systems.
  • Enterprise AI risk emerges primarily at the identity and integration layer, not just the model layer.
  • Point-in-time compliance checklists fail in SaaS environments; governance must operate continuously.
  • Grip’s 5-stage framework transitions organizations from basic discovery to automated enforcement.

‍

What Is an AI Governance Framework?

An AI governance framework is a structured set of policies, technical controls, and continuous monitoring processes designed to manage enterprise risks across artificial intelligence models, SaaS integrations, and autonomous agents. It enforces identity-first security, manages machine entitlements, and ensures regulatory compliance without hindering business innovation.

An AI governance framework is an operational architecture of policies, identity-centric controls, and continuous monitoring processes designed to discover, evaluate, and enforce security across all AI models, agentic workflows, and SaaS-connected AI tools. While traditional IT governance relied on static checklists, modern AI governance operates continuously to mitigate risks from shadow SaaS and rogue AI, non-human identity (NHI) privilege creep, and unauthorized data ingestion.

‍

Want to discover your shadow AI tools today? See how Grip maps unmanaged agents. Book a Demo →

The 5-Stage Framework for Continuous AI Governance

Effective AI governance cannot stop at written acceptable use policies. Grip Security establishes a five-stage operational progression that moves organizations from visibility to continuous control:

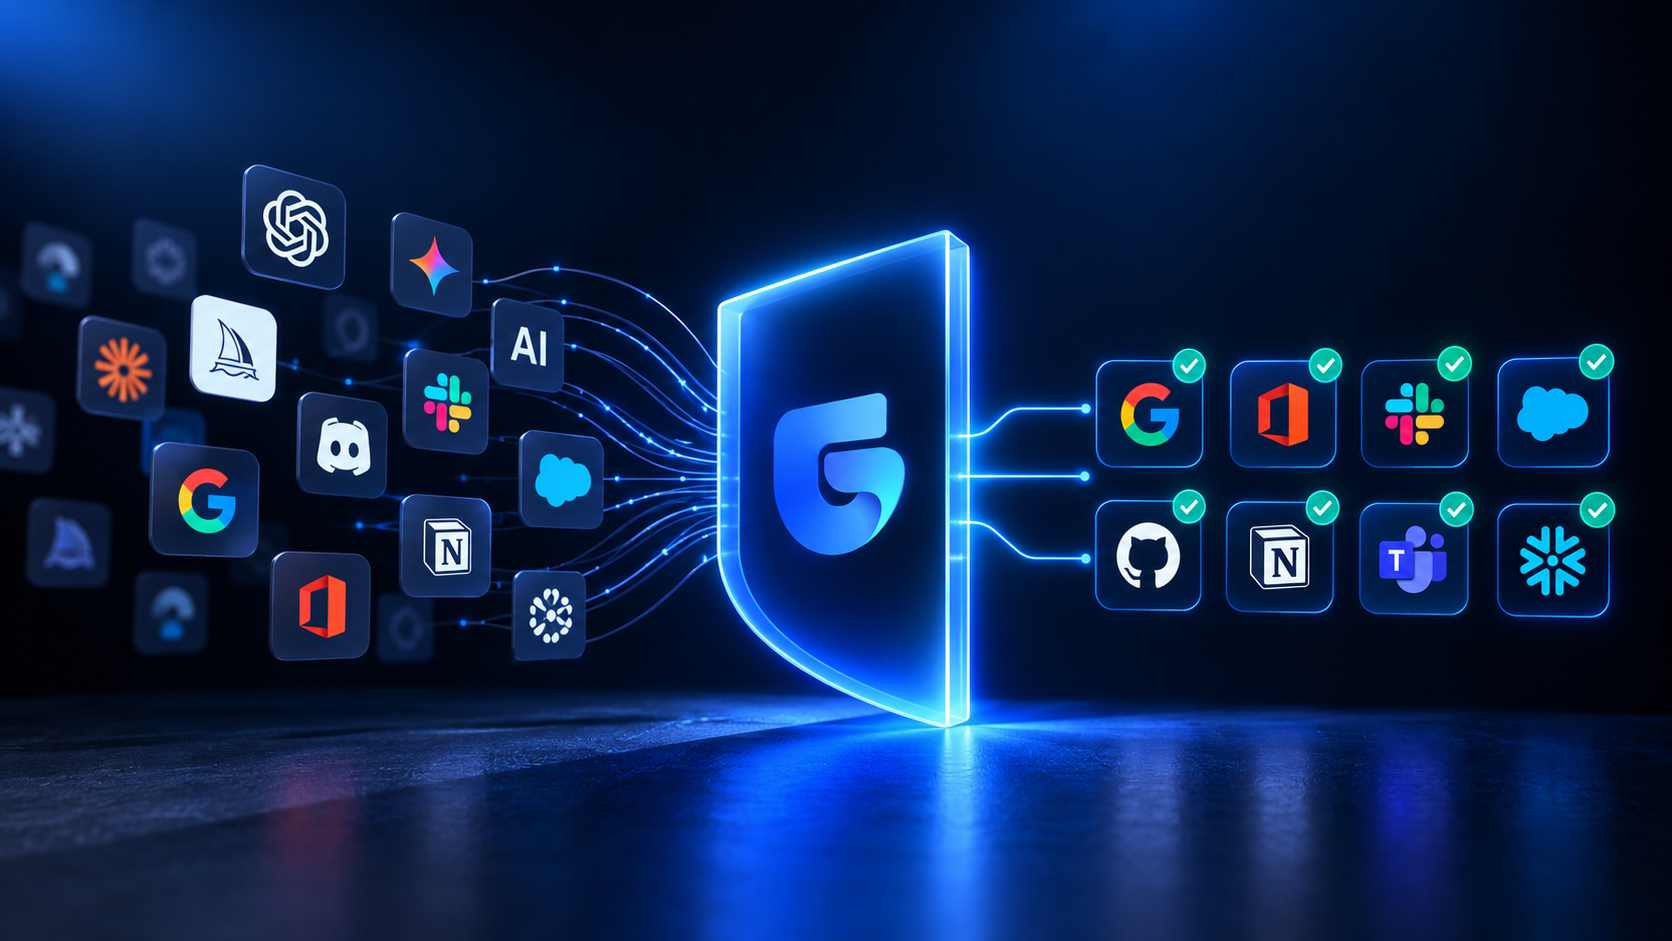
  1. Visibility: Continuous, agentless discovery of every AI tool, browser extension, and agentic workflow active across the workforce—illuminating unmanaged shadow AI.
  2. Context: Mapping which human and non-human identities are accessing AI, what permissions they hold, and which external SaaS databases are connected.
  3. Governance: Aligning usage with regulatory standards like the EU AI Act and NIST AI RMF, defining acceptable risk thresholds and data handling policies.
  4. Enforcement: Applying automated controls such as revoking risky OAuth grants, blocking unauthorized AI connections, and enforcing least-privilege access.
  5. Continuous Control: Real-time telemetry to detect posture drift, abnormal token usage, or emerging shadow agents before exposure occurs.

‍

Core Principles of Enterprise AI Governance

To implement an effective program, organizations should adhere to four architectural principles:

  • Identity as the Control Plane: Because AI tools act through credentials and tokens, identity is the single most reliable enforcement boundary.
  • Separation of Policy and Enforcement: Policies provide guidelines, but automated enforcement mechanisms must exist in software to stop risk in real time.
  • Continuous Over Static: Annual audits are insufficient when employees onboard dozens of new AI services every month.
  • Zero-Friction Discovery: Avoid heavy agents or network proxies that degrade user experience and trigger bypasses; prioritize identity-first observation.

‍

Frequently Asked Questions

What is the difference between AI security and AI governance?

AI security focuses on protecting AI systems from technical threats (e.g., prompt injection, model poisoning, and token theft). AI governance focuses on policies, organizational accountability, data handling compliance, and acceptable use. In practice, governance sets the boundaries that security enforces.

How often should an enterprise AI governance framework be audited?

Because enterprise SaaS and AI adoption move at cloud speed, AI governance cannot rely on annual reviews. Security teams should implement continuous automated monitoring of AI discovery, token grants, and data flows to ensure ongoing compliance.
Grip Security
Ready to Automate Your AI Governance Framework?
Discover shadow AI tools, enforce least-privilege agent access, and secure SaaS identities across your enterprise in minutes.
Book a Demo →

Evaluating SSPM Platforms? See Grip's Identity-First Control Plane

Compare Grip live against legacy SSPMs.
Discover unmanaged AI and SaaS across the environment.
Govern non-human identities and hidden OAuth risk.
Continuously remediate identity and access exposure.
See the full attack surface in one control plane.

See Grip's Control Plane in Action

Book a Demo