
Shadow AI is the unsanctioned use of AI tools or features inside SaaS apps. It occurs when employees enable new AI capabilities or adopt AI apps without IT review or formal vetting, creating unmanaged identities and data exposure across cloud services.
This includes generative AI tools accessed through personal accounts, third-party LLM platforms used outside approved environments, and AI features activated within existing SaaS applications without security oversight.
In most cases, shadow AI is not intentional misuse. It is a byproduct of employees moving faster than governance, filling gaps between what approved tools provide and what the business demands.
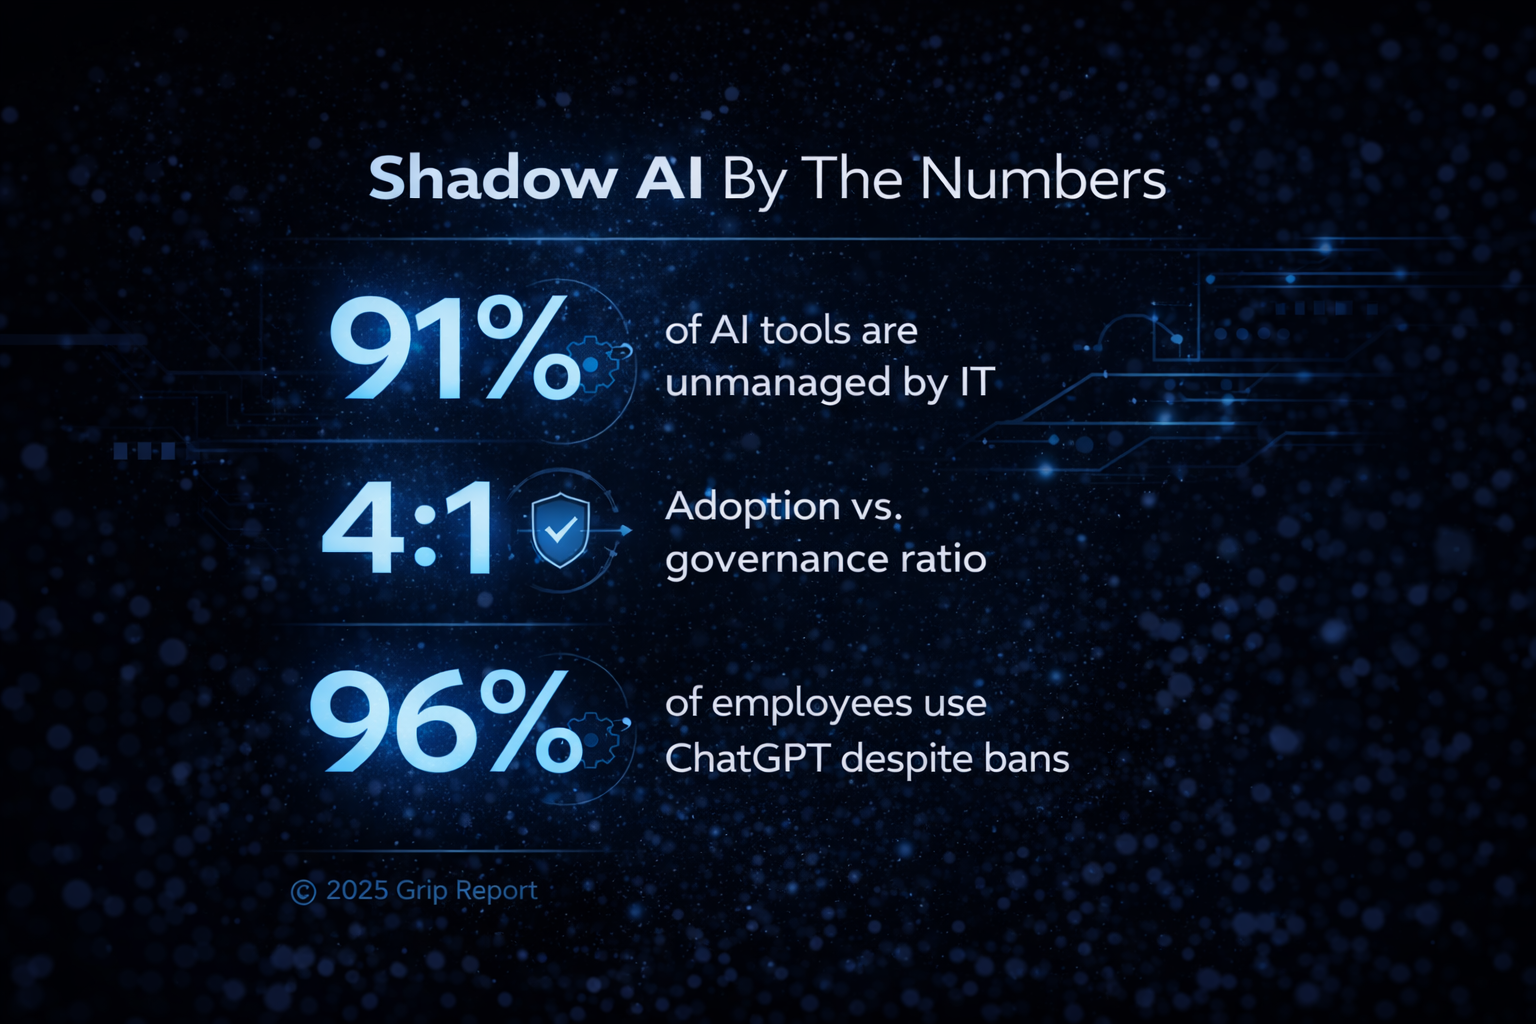
According to Grip's 2025 SaaS Security Risks Report:
These findings show AI is embedding into SaaS faster than controls can keep up, widening the visibility and governance gap.
Read the full report for more on shadow AI and shadow SaaS.
Want to discover your shadow AI tools today? See how Grip maps unmanaged agents. Book a Demo →
The risks of shadow AI fall into three categories.
First, data exposure. Sensitive information such as customer records, source code, or internal documents is often entered into AI tools with unclear storage, retention, or training policies.
Second, regulatory and compliance risk. When data leaves approved systems or crosses geographic boundaries through AI tools, organizations risk violating frameworks like GDPR, HIPAA, or emerging AI governance standards.
Third, identity and access risk. Shadow AI tools introduce non-human identities, API keys, and browser extension tokens operating outside single sign-on (SSO) and multi-factor authentication (MFA) controls.
These risks are amplified because shadow AI is dynamic. An employee might begin using an AI tool for simple task automation, but over time, that tool is connected to file storage, messaging platforms, or corporate email, expanding the attack surface.
Shadow IT is the broader umbrella. Shadow AI is a distinct subset with unique risks.
Shadow IT encompasses any unsanctioned technology, including cloud storage apps, project management software, and personal devices. The primary risks of shadow IT center on unmanaged data silos and lack of visibility.
Shadow AI introduces additional risks. Unlike standard software, AI tools often consume, process, and retain data for model training. Generative AI tools can extract context and infer relationships across datasets. Additionally, AI agents increasingly act autonomously, executing tasks and making decisions based on inputs they receive.
In other words, where shadow IT involves unmanaged software, shadow AI involves unmanaged intelligence.
Traditional network security tools struggle to detect shadow AI. Modern AI tools are browser-based, cloud-hosted, and often accessed through valid credentials, making them appear as standard web traffic.
Addressing shadow AI requires a modern, identity-first approach:
By prioritizing visibility and governance rather than blunt blocking, security teams can enable business productivity while protecting critical assets.
Examples include employees using consumer AI chatbots like ChatGPT or Claude for work tasks, installing unauthorized AI-powered browser extensions for writing assistance, or connecting third-party AI meeting summarizers to corporate calendars.
Shadow AI exposes organizations to data leaks, compliance violations, and identity vulnerabilities. Because these tools operate outside IT visibility, security teams cannot enforce access controls, monitor data flows, or revoke access when employees depart.
Blocking AI tools rarely works; employees typically find workarounds. Instead, organizations should deploy identity-first security solutions that discover shadow AI usage, assess risk, and provide pathways to safely sanction or manage tools the business needs.
Employees are moving fast with AI. Blocking it stifles innovation, but ignoring it creates unacceptable risk. Grip's SaaS Security Control Plane provides continuous discovery of every AI tool, extension, and non-human identity in your environment—even when accessed via personal accounts or unmanaged devices. With complete visibility, you can pinpoint high-risk tools and prioritize next actions (e.g., SSO/MFA enforcement, scope reduction, token revocation, or access removal). You regain control without stifling innovation. See how Grip reduces shadow AI risks, then take the next step and book a demo with our team.


Gain complete visibility into unmanaged AI tools, autonomous agents, and hidden OAuth permissions before they expose enterprise data. Deploy in minutes with zero disruption.
 Book a Live Demo →
