Fix SaaS Misconfigurations

Find and remediate misconfigurations in critical SaaS apps.

​Quickly identify, prioritize, and fix risky misconfigurations in business-critical SaaS like Microsoft 365, Google Workspace, Salesforce, and more.

Misconfigurations are the third most common error in a breach​

Many organizations incur incidents due to SaaS misconfigurations. Grip safeguards your SaaS by proactively identifying and correcting your application and identity vulnerabilities.

Automate SaaS misconfiguration management.​

Reduce manual effort by automating detection and remediation, eliminating time-consuming, error-prone manual assessments.​

Book a Demo
Offboarding screenshot from Grip's platform
Dashboard displaying severity levels of SaaS misconfigurations with status indicators for various policies.

Continuously detect SaaS misconfigurations.​

Get full visibility into your SaaS posture.​

Grip continuously scans and detects misconfigurations, identifying drift in SaaS posture that can lead to breaches.​

Prioritize what matters.​

Understand which users or apps authorized specific scopes and their capabilities, to make informed decisions aligned with your risk tolerance.

Fix SaaS misconfigurations with confidence.​

Get security-backed recommendations.​

Fix configurations with clear guidance based on leading frameworks like NIST.​

Collaborate for faster resolution.​

Automate workflows to engage app owners and secure apps proactively.​​

Track progress.​

Monitor real-time metrics and easily share security improvements with stakeholders.​
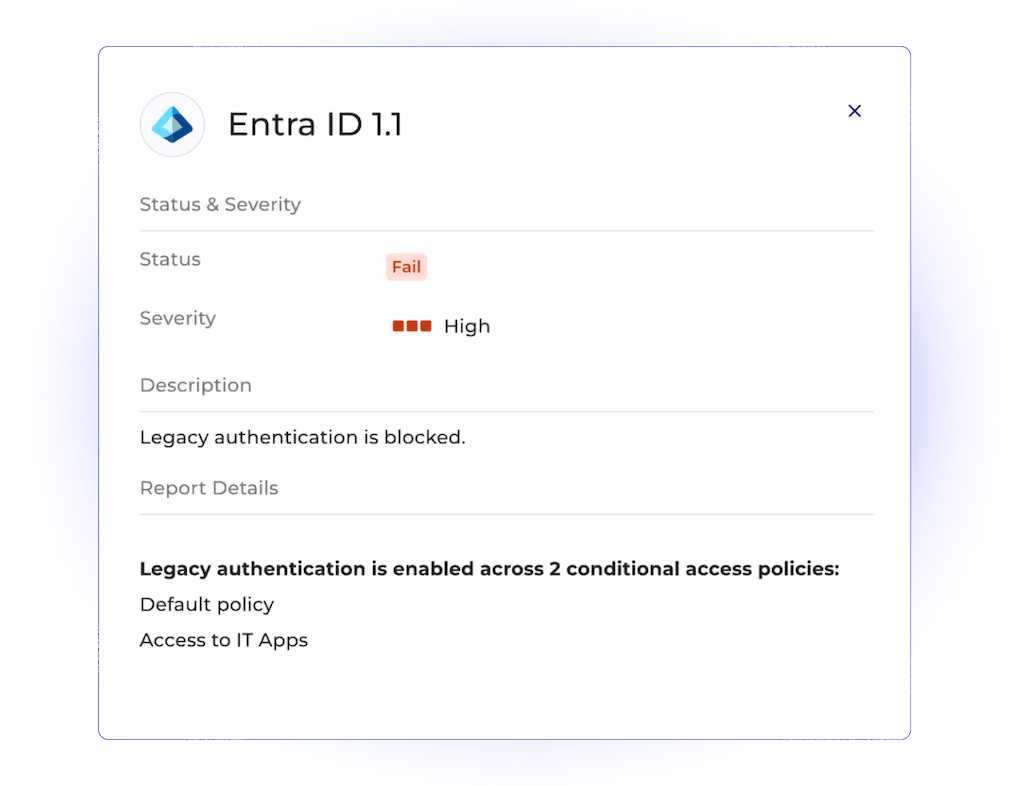
Entra ID 1.1 UI showing a high severity status for blocked legacy authentication in SaaS security.

Take the next step in securing your SaaS environment.​

Move from unmanaged SaaS risk to a proactive approach to SaaS security. Discover how Grip empowers you to efficiently govern, secure, and manage SaaS risk, without adding complexity or extra headcount.​

Book a Demo:​

How is Grip SSPM different?

Grip SSPM is just one part of a holistic SaaS security strategy. Securing individual apps isn’t enough—the real challenge is managing how SaaS is adopted, as employees continuously introduce new tools without proper security. Grip’s offers a complete platform that goes beyond SSPM, providing full visibility, control, and protection across the entire SaaS ecosystem.

Why is SSPM important?​

SaaS misconfigurations and lack of visibility create significant risks for businesses. Studies show that misconfigurations are the third most common error in a breach. With multiple teams often adjusting SaaS configurations without understanding the security impact, continuous monitoring and automated remediation are essential to maintaining a secure posture.

What are the top challenges in managing SaaS posture?​

Managing SaaS posture is difficult due to limited visibility into application configurations and changes, which creates blind spots. Many organizations still rely on manual audits—over 48%—which are slow, error-prone, and resource-intensive. Additionally, teams often lack the bandwidth and expertise to address misconfigurations across a growing number of SaaS applications.​

How does automation improve SaaS security posture management?​

Automation streamlines detection and remediation processes. Organizations using SSPM tools check settings 78% more often and resolve misconfigurations 73% faster than manual methods. Automation also prioritizes critical issues, saving time and reducing errors.​

FAQs about SSPM​